Security planning should consider what happens if a control fails. Prevention remains important, but a business also needs ways to detect suspicious activity, limit access, respond to an incident, and restore operations. An assume-breach approach helps organize those decisions.
Start with the systems and information that matter
Identify the applications, accounts, devices, and information the business depends on. Review who can access them, who administers them, and which outside providers are involved. This gives the team a practical basis for setting priorities.
Use identity and device controls together
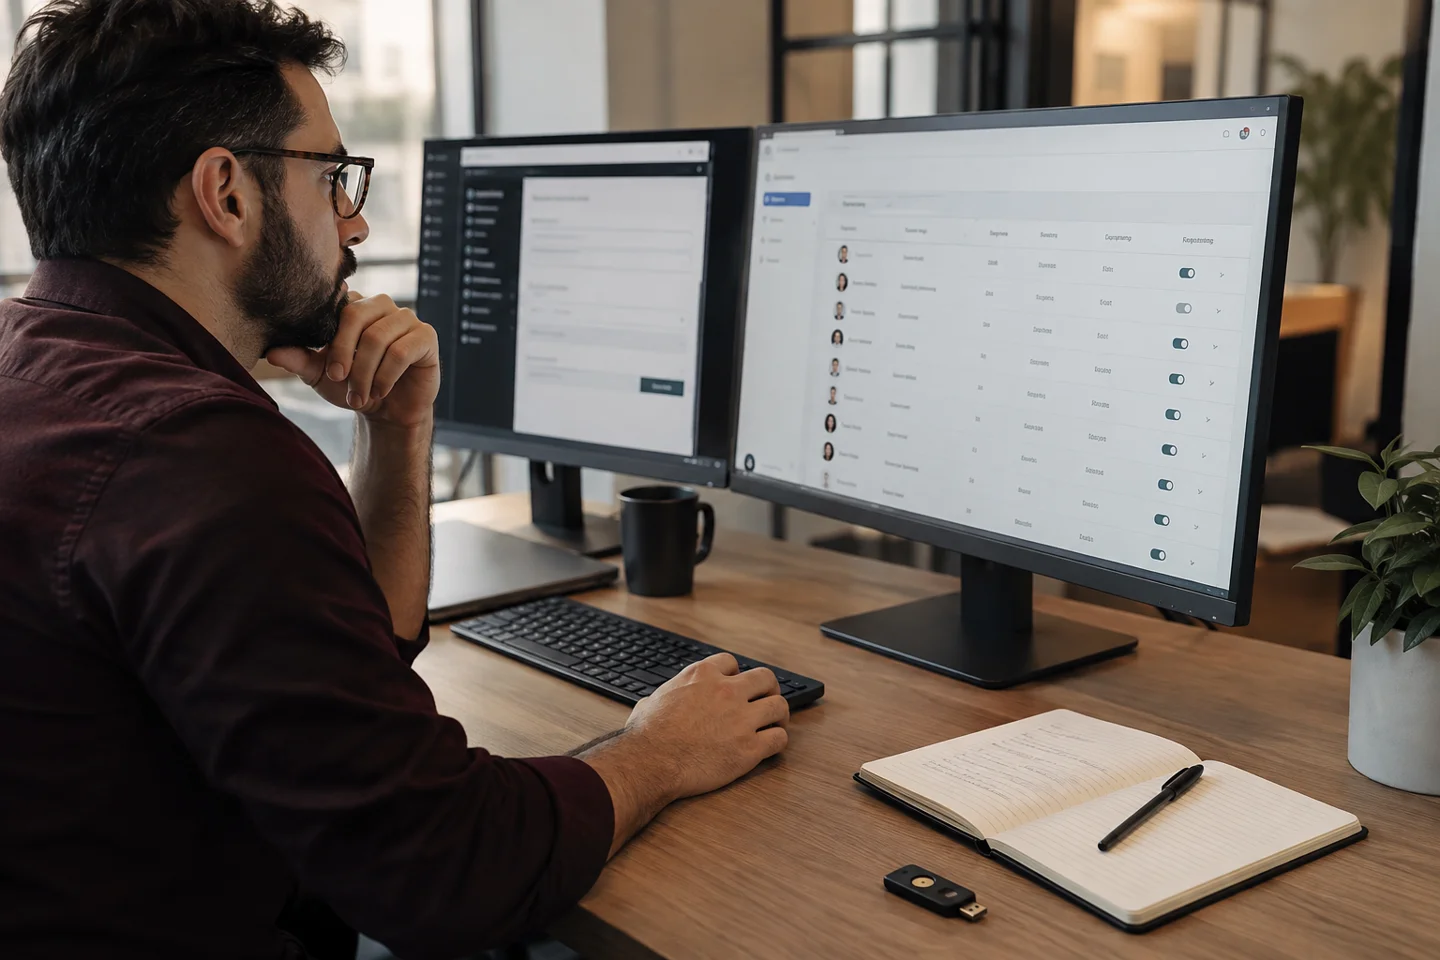
Multifactor authentication, appropriately scoped permissions, managed devices, and access policies can reduce exposure. Their usefulness depends on the environment, licensing, configuration, and ongoing administration. No individual control guarantees that an account or system cannot be compromised.
Review privileged access separately. Limit it to the people and tasks that need it, protect the accounts involved, and remove access when responsibilities change. Where the platform supports it, consider time-limited administrative access.
Limit the paths between systems
Avoid assuming that a person or device should reach every resource simply because it has connected to the network. Review application permissions, shared accounts, remote access, and vendor access. Appropriate segmentation and least-privilege access can help limit the scope of an incident.
Agree how detection leads to a response
A monitoring tool needs an operating process behind it. Clarify which alerts are reviewed, who investigates, who can approve containment actions, and how the business will be contacted. Some response actions can be automated within agreed boundaries; others need human judgment.
Match support and monitoring arrangements to the business. Standard business-hours support and extended coverage are different service commitments. Document the arrangement rather than assuming every urgent situation receives the same response.
Make recovery a business discussion
Identify what needs to be restored first, the dependencies involved, and who can authorize the work. Discuss backup scope, retention, recovery expectations, and testing. Backup and recovery services should be clearly defined; the presence of a backup job alone does not demonstrate that a business can restore the required operation.
Choose priorities that can be maintained
Zero Trust is a set of principles applied across identity, devices, applications, networks, and data. It is not a single product or a promise of complete protection. Start with the gaps that matter most, assign ownership, and review the controls as the business changes.
Huneidi can help review the environment, coordinate vendors, and propose security and management work within an agreed scope. The aim is a clearer operating plan: what is protected, who responds, and how the business prepares for disruption.